Our department received a call from a civilian, who was apart of a “to catch a predator group”, reporting a suspect who was seeking to meet a child. The suspect provided the passcode to their phone but shortly afterward requested an attorney therefore ending our interview.
Given the allegations and the high potential for CSAM to be present on the device, we obtained a search warrant and contacted the Federal Bureau of Investigation to perform an extraction of the device. We also wanted to determine whether the FBI had an interest in the case and potentially pursuing federal charges.
We received the device back after Special Agents advised that they had attempted multiple extractions over the course of approximately a week using both GrayKey and Cellebrite. Despite their efforts, the extractions repeatedly stalled, and they were unable to successfully retrieve the data.
Before resorting to manually extracting evidence from the device, we attempted an acquisition using DATAPILOT X. Within a single shift, we successfully obtained a full acquisition of the device.
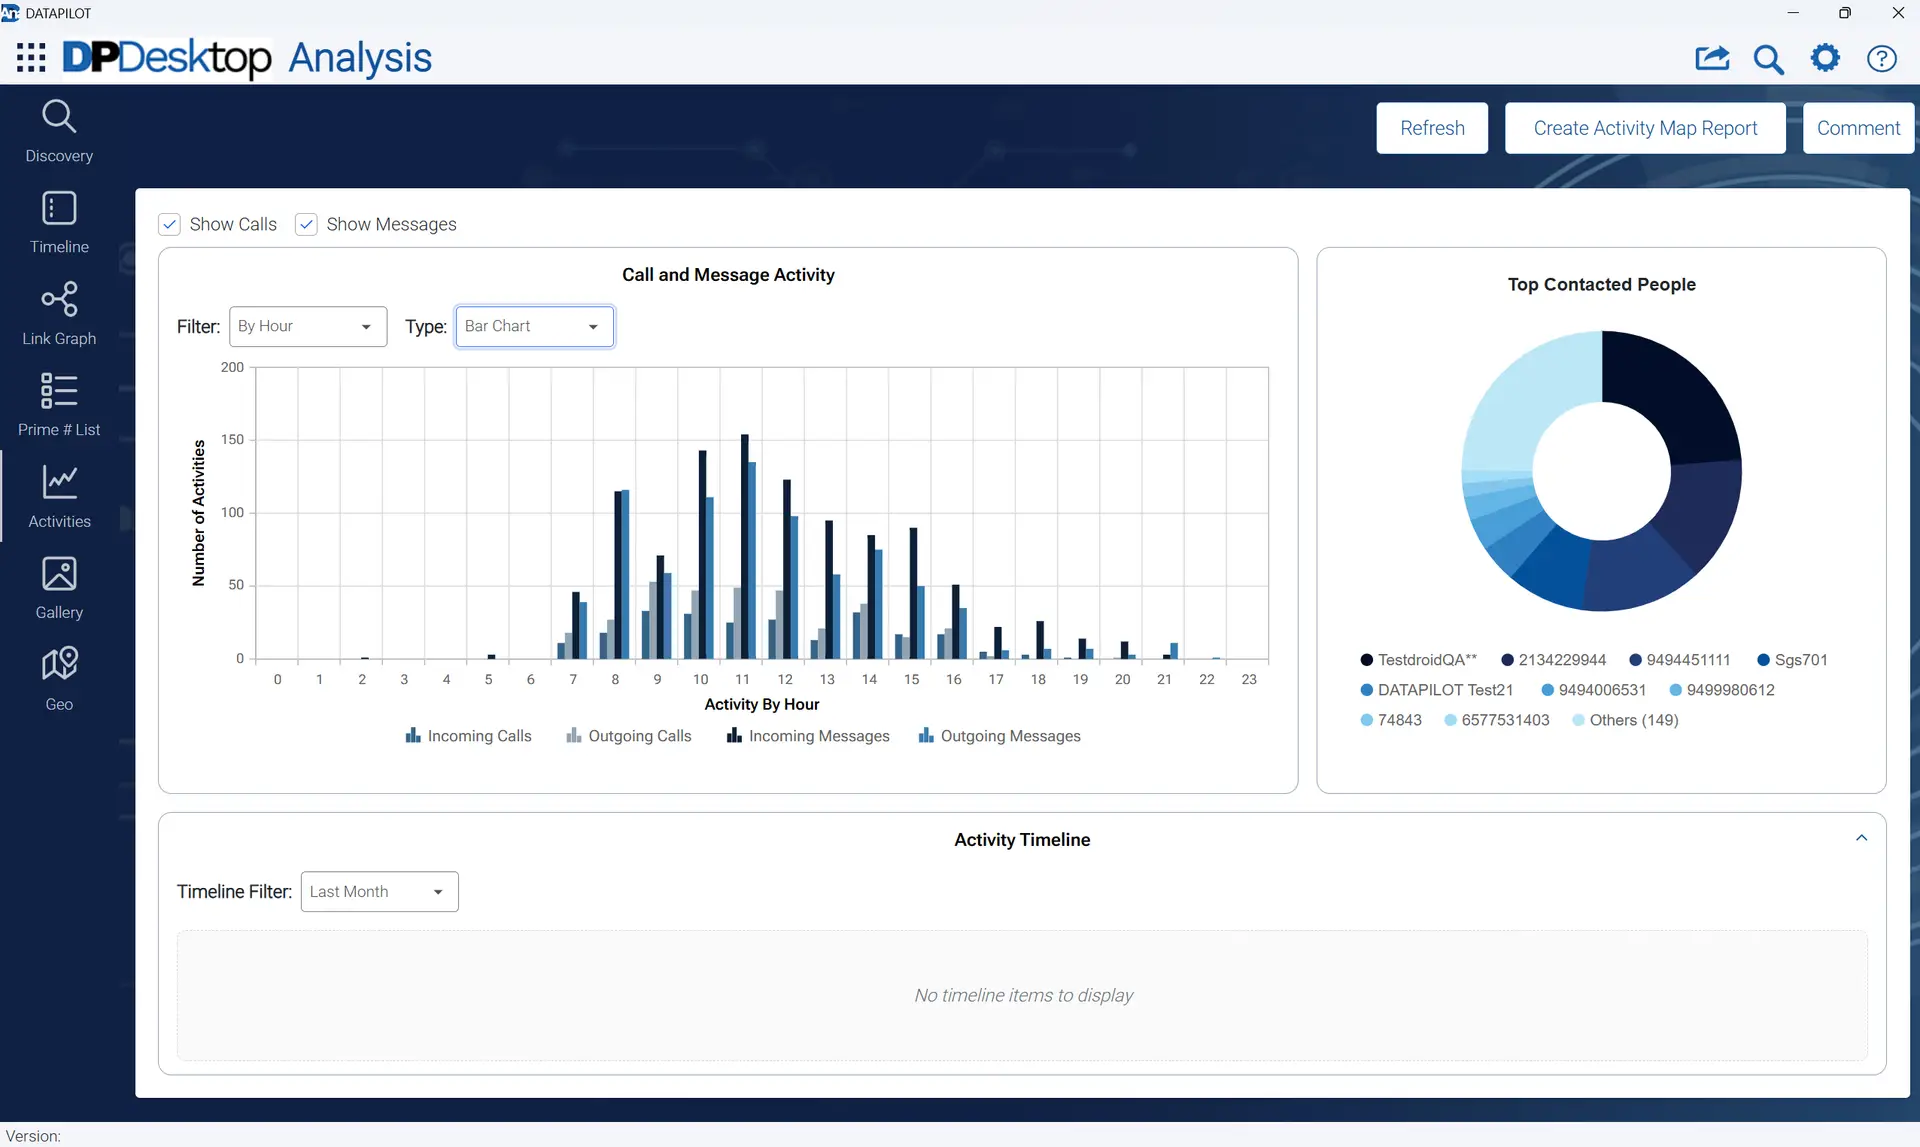
DATAPILOT successfully extracted more than 30,000 images and 2,600 videos, many of which were stored within Telegram messages and Hidden Albums on the device. Following an extensive analysis with DATAPILOT Desktop, the full report was condensed into a concise discovery report that was easy to share with the District Attorney’s Office and clearly documented numerous instances of CSAM being possessed and shared.
The case initially appeared to be at a dead end when we received the device back from the FBI without a successful extraction. However, DATAPILOT changed the trajectory of the investigation. Because of DATAPILOT, we were able to preserve critical evidence and move forward with a much stronger case.